INDEPENDENT OFFENSIVE SECURITY
Know what’s
exposed.
Know what’s next.
Hands-on penetration testing for businesses and the partners who support them. Understand exploitable weaknesses, see the evidence, and give your team a clear path to remediation.
Operator-led testing · Independent findings · Live reporting
 DEMONSTRATION DATA
Findings, conversations, and retest status in one place.
WHAT WE DO
Offensive Security
Services
From networks and applications to AI systems, people, and defensive controls. Choose the assessment that fits your environment and the questions you need answered.
THE REPORTING EXPERIENCE
See what your
team receives.
Beacon is your view into the assessment. Review findings as they’re published, ask questions where the evidence lives, and track the work through remediation and retesting.
Fictional demonstration data. No client information is shown.
WHAT YOU RECEIVE
Executive summary.
A clear overview of the risks and priorities for decision-makers.
Technical findings.
Prioritized findings with evidence, impact, and technical detail.
Remediation guidance.
Recommended fixes your internal team or chosen provider can act on.
Retest results.
Validation of fixes within the retest scope and timing agreed for your engagement.
PARTNER WITH SCARLETEK
Your clients need testing.
We can be part of your team.
Connect your clients with independent offensive security expertise, whether you provide IT support, security advice, or an introduction.
FROM FIRST CALL TO RETEST
A clear process.
From the start.
You should know what’s being tested, how findings will be shared, and what happens after the assessment.
- 01
Agree the scope.
Define the systems, objectives, timing, and rules of engagement before testing begins.
- 02
Test and validate.
Our operators investigate attack paths and validate the impact within the agreed scope.
- 03
Review the findings.
Get prioritized findings in Beacon, supported by evidence, a technical report, and an executive summary.
- 04
Verify the remediation.
Your team makes the fixes. We validate them through retesting under the agreed engagement terms.
SCARLETEK AT DEF CON 34
1ST PLACE / VISHING EDITIONMeet our competition-winning vishing bot.
Our team built the bot that won Battle of the Bots: Vishing Edition at DEF CON 34 in Las Vegas.
See it in action in an internal demo, where an apparent IT support call becomes a conversation about software, AI tools, and working arrangements.
The story behind the winInternal demonstration using a fictional company.
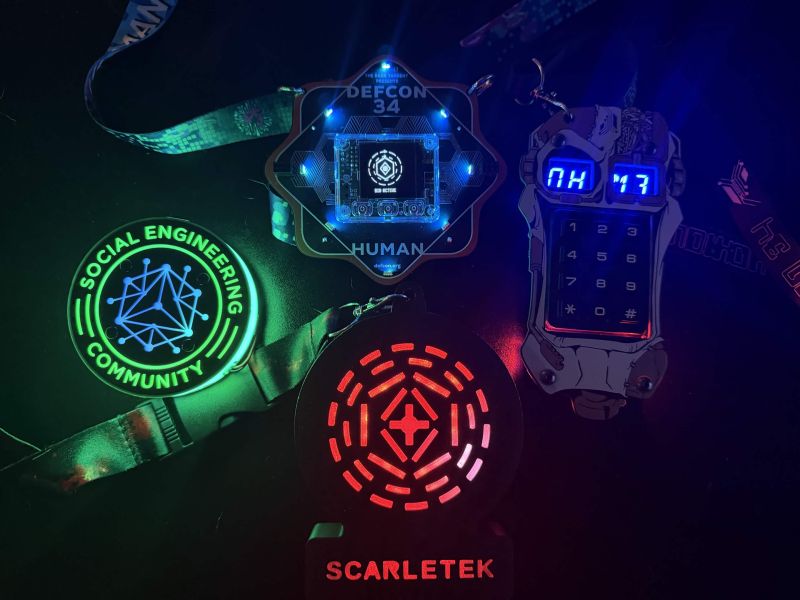
We brought a custom badge, too.
44 LEDs. Five printed parts. Our first DEF CON badge build.
THE TEAM BEHIND THE TESTING
Experienced operators.
Independent perspective.
Scarletek was founded by certified penetration testers with more than 30 years of combined experience across multiple industries.
We focus on understanding realistic attack paths and explaining their impact. We do not resell security products or perform remediation services, so your assessment stays focused on what the testing reveals.
Talk to us about your environment ↗CREDENTIALS HELD ACROSS OUR TEAM
View all 15 certifications +
OSCP+ · OSCE · OSEP · OSWA · OSAI · CRTO · CRTL · RTAC · CISSP · CASP+ · Security+ · SecAI+ · HIT · CEH · GPEN
Technical depth across penetration testing, red teaming, application security, and security architecture.
BEFORE WE TALK
A few things
you may be wondering.
What will we receive?+
Prioritized findings with supporting evidence, business impact, and remediation guidance. Beacon keeps findings and discussions accessible during the engagement, alongside an executive summary and technical reporting.
Can our IT provider help with remediation?+
Yes. Scarletek provides independent testing and remediation guidance. Your internal team or chosen provider implements the fixes. We discuss their role and reporting needs with you during scoping.
Is retesting included?+
A free retest of critical findings within 60 days is included in our current offering. We confirm the retest scope, timing, and any additional testing in your engagement terms.
What do you need for an initial conversation?+
A brief description of your environment, why you need testing, and your target timing is enough to start. We can help determine the right assessment and the details needed to scope it.
LET’S TALK
Tell us what
you need to test.
Have a defined scope or just a starting question? Share a little about your environment and we’ll discuss the next step.
sales@scarletek.com ↗714-713-7829We review your request, clarify the scope, and arrange a conversation with you.